Who this is for
Risk and compliance, Leadership.
Start with the challenges your team faces and each person’s current skills.
How to structure an AI governance workshop around responsibility, data boundaries, human oversight, practical scenarios and the limits of training alone.
AI governance workshops: Practise policy decisions, risk identification and human review using a bounded workplace scenario.
Risk and compliance, Leadership.
Start with the challenges your team faces and each person’s current skills.
A scenario decision record with an escalation path.
This is an example to help scope the learning; delivery arrangements are agreed before booking.
Describe the task, affected people, data boundaries and decision owner.
Identify unreliable output, sensitive information and situations requiring escalation.
Compare responses to a scenario and record the rationale for a bounded decision.
Identify unresolved questions, control owners and evidence needed before implementation.
Use these stages to discuss the learning scope. Timing, tools and exercises depend on the team’s brief.
Describe the task, affected people, data boundaries and decision owner.
Identify unreliable output, sensitive information and situations requiring escalation.
Compare responses to a scenario and record the rationale for a bounded decision.
Identify unresolved questions, control owners and evidence needed before implementation.
Bring the relevant internal policy, a fictional or approved workplace scenario, and the roles responsible for reviewing AI use.
Estimate the time your team needs for sessions and follow-through. Change the example to fit your people; this is not a workshop package or quote.
Compare programs against your challenge, audience and available time. Confirm the actual schedule and fees with the organizer.
Find relevant programs in AISFYYou may need to sign in. Results stay on this page and are not saved or transferred to your AISFY account. Copy your plan before continuing.
Cohorts = participants ÷ cohort size, rounded up. Per-person time = session hours + weekly practice × weeks. Team time multiplies that by participants. Delivery hours count repeated sessions across cohorts; they exclude facilitator preparation.
Defaults are illustrative inputs, not benchmarks or recommended commitments. Changing or leaving the page resets the plan.
Open a topic for the full guidance, examples and references.
The 2026 AI Index reports 362 documented AI incidents in 2025, compared with 233 in 2024 in the AI Incident Database. Stanford HAI — AI Index 2026, Responsible AI.
Evidence limits: Recorded incidents depend on reporting and coverage. These counts do not measure the probability that a particular organization’s use case will cause harm.
Use an incident to trace the decision that allowed harm, not merely to make the session alarming. Identify the information available, the person responsible and the point where the process could have stopped. Reporting counts provide context but cannot assign a risk score to your organization.
Consider a fictional employee sending an unverified AI-generated policy summary to a customer. Record the failure as an unsupported external statement. Assign a source-checking step, an accountable reviewer and a retained approval record. Test the control with another summary containing a subtle date error before calling the control effective.
Sources checked 20 October 2026. External examples are not AISFY customer results. Practice scenarios are editorial examples.
Participants explain a decision, identify a boundary and describe when to stop or escalate.
Teams need more than definitions of fairness, transparency and risk. They need to recognise the decisions that arise in ordinary work: what information may enter an AI tool, what requires verification, who owns the output and when a human must intervene.
Every scenario should identify a human owner. Participants should be able to explain who requested the work, who reviews it, who is affected and who has authority to approve or stop the next action.
Use role-relevant examples involving confidential information, inaccurate outputs, automated communications, consequential decisions and unclear ownership. Ask participants to classify what is allowed, what requires review and what should not proceed.
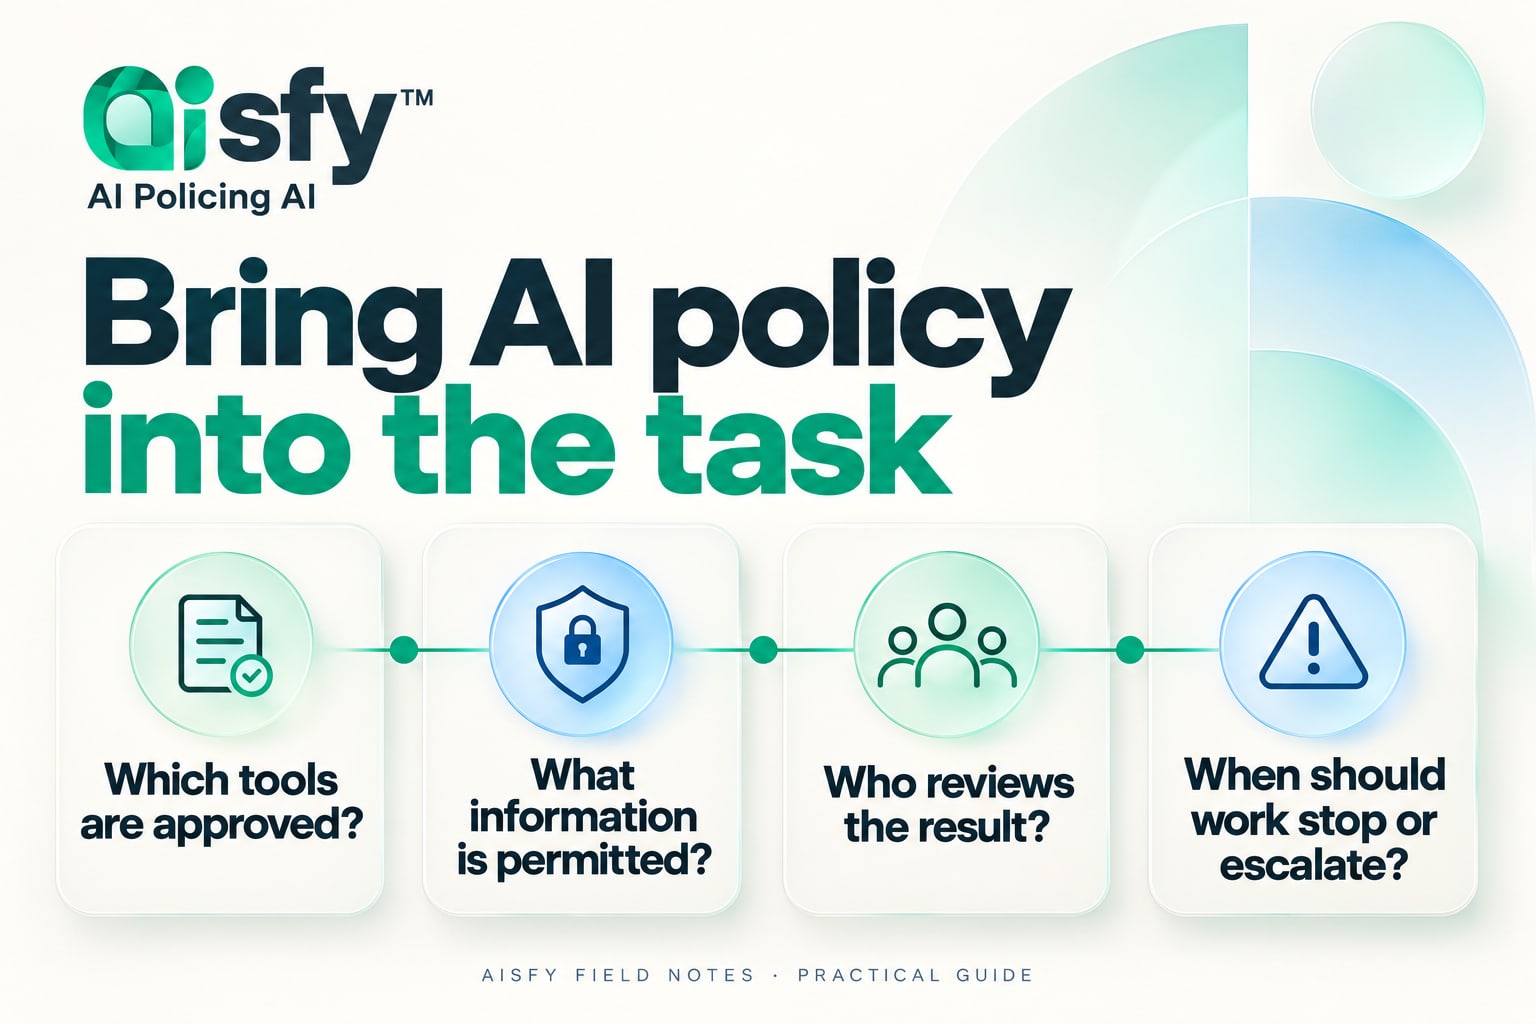
Policies become useful when people can translate them into tool choice, data handling, review and escalation behaviour. The workshop should identify where policy is clear, where it is missing and which controls require implementation outside the training room.
Training can build awareness and responsible habits. It does not create a complete AI governance system. Formal risk classification, approval chains, policy controls, escalation records and organization-wide audit requirements need their own owners and implementation.
Useful outputs include documented scenarios, agreed responsibilities, identified policy gaps and a list of decisions requiring operational controls. These records can guide the next governance step without claiming that the organization is fully governed.
Choose three fictional or approved situations that participants can recognize: summarizing a restricted document, drafting a message for an external recipient and using an AI recommendation in a decision affecting someone. Supply a short policy excerpt with each scenario. Ask participants to identify the input, affected people, reviewer and authorization required.
Change one condition at a time. An internal draft becoming an automatic external message changes the risk and permission boundary. A public source replaced by confidential customer data changes the access question. This method helps participants explain their decisions instead of memorizing a fixed answer.
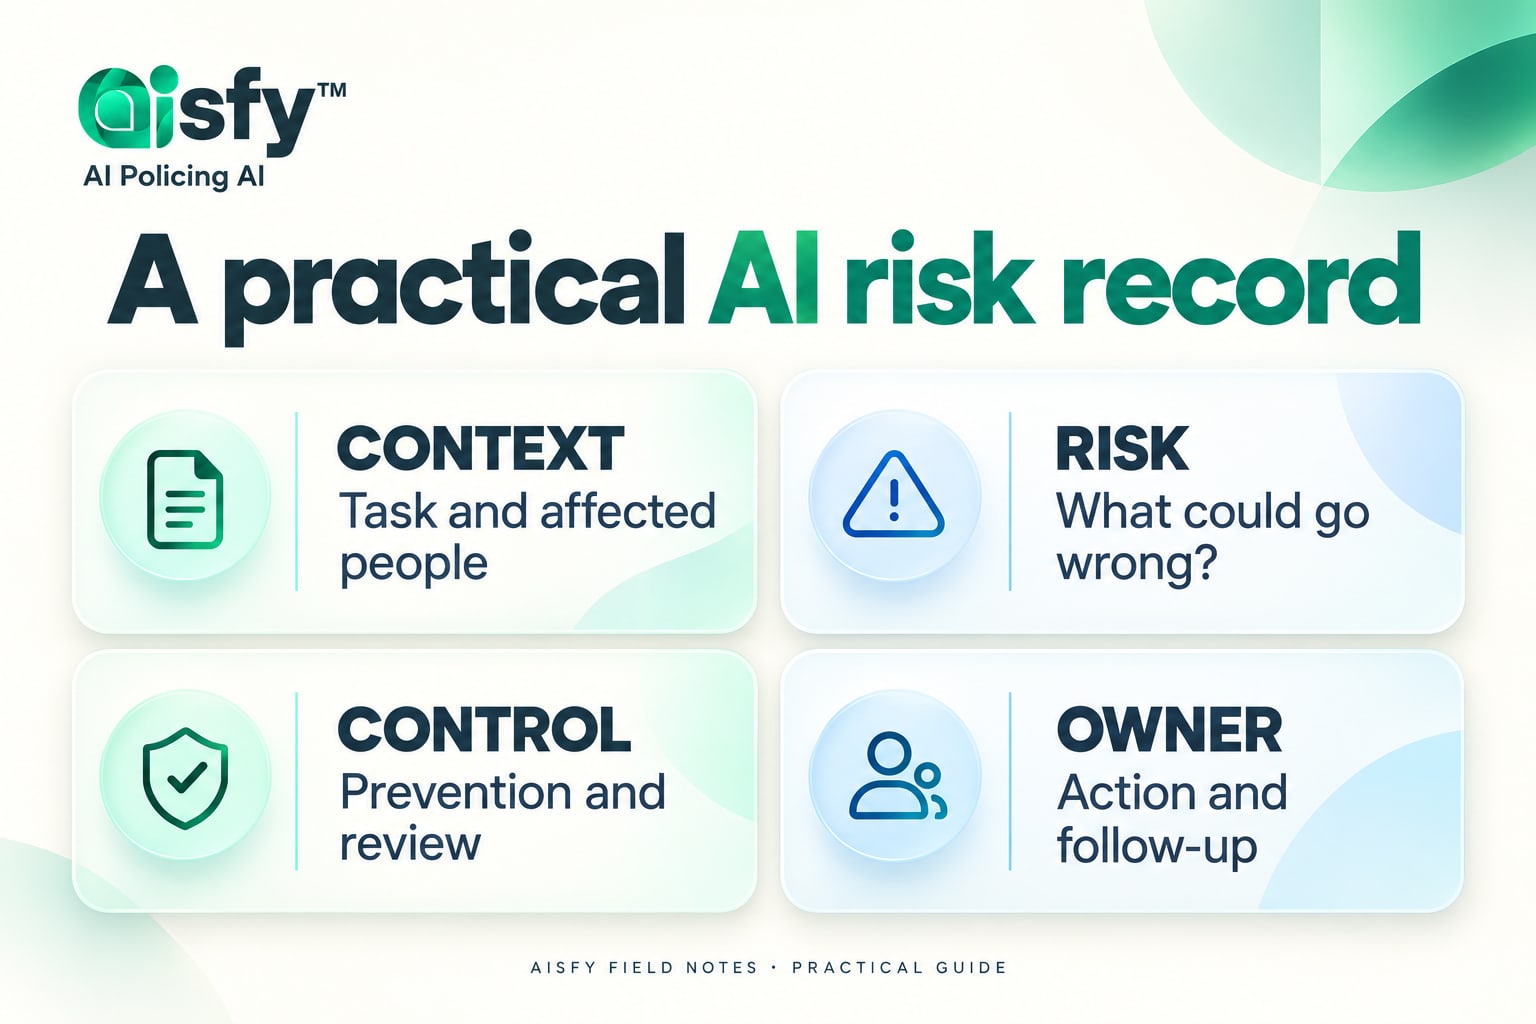
For each scenario, record the business owner, permitted tool, data classification, output reviewer, decision-maker and escalation route. Add a field for unresolved questions. If a role cannot be named, the exercise has identified a real gap; do not fill the box with a generic label such as “the business” and treat it as resolved.
A responsibility worksheet supports discussion. It is not evidence that a control is implemented in software or that the assigned person has accepted the role. The authorized owner must validate proposed responsibilities and determine how they connect to existing policy.
Give participants a new scenario after the discussion and ask them to explain whether they would proceed, adapt the task or stop. Review the reasoning against the supplied policy. A participant who correctly declines an inappropriate use has demonstrated something valuable even though no AI output was produced.
Record recurring misunderstandings and route them to the relevant owner. A question about contract terms needs an appropriate specialist; a missing access control may require IT work. These should not disappear into a general training-completion statistic.
The voluntary NIST AI Risk Management Framework can help organize questions about context, ownership and risk through Govern, Map, Measure and Manage. A workshop can use those questions as a learning structure. Participation does not constitute a NIST certification or a legal opinion.
For jurisdiction-specific requirements, use current official sources and qualified advice. The facilitator should distinguish general responsible-use practice from obligations that depend on the organization, sector, location or use case. Record those dependencies in the follow-up plan.
For workshop options, explore enterprise AI workshops. Use the preparation checklist and evaluation guide to connect the session to a practical next step.
Reference: NIST AI Risk Management Framework.
Employees encounter governance as a practical question: may I use this document, send this draft, or rely on this recommendation? A list of principles helps only when people can connect it to a real decision. The workshop should therefore begin with a small set of tasks and the policies that govern them.
AISFY enquiries for this workshop should identify the teams involved and the decisions causing uncertainty. The proposed scope can focus on awareness, scenario practice or policy-gap discovery. Legal interpretation, formal assurance and implementation of technical controls require appropriately qualified owners and separate scope.
Invite a business process owner and representative users, with risk, compliance, privacy, information security or IT participation where relevant. The purpose is not to ask every stakeholder to approve every output. It is to establish which decisions need specialist review and which can be handled through a clear working rule.
Before the session, request approved policy excerpts, a list of permitted tools and two or three sanitized scenarios. Where a policy is missing, mark the exercise as unresolved instead of inventing permission in the room.
In a fictional example, a customer-service manager wants to summarize complaints with a general AI assistant. The source contains names, health-related comments and contract details. Participants must decide whether the data may be used, what alternative material is suitable, who approves the environment and what must be checked before the summary informs a decision.
Then change one condition: the assistant proposes emailing its summary automatically. The group must reassess authorization, recipients, review and the ability to stop the action. This exposes the difference between producing a draft and allowing a system to act.
| Stage | Participant activity | Evidence to retain |
|---|---|---|
| Map the task | Identify input, output, affected people and decision owner | A task and responsibility map |
| Test data boundaries | Classify sample inputs against existing policy | Allowed, restricted and unresolved material |
| Review output | Find unsupported claims and inappropriate recommendations | A review checklist with failed examples |
| Escalate uncertainty | Decide who must resolve each open issue | Named issues and escalation owners |
| Agree follow-through | Select one policy clarification or controlled practice task | A bounded action list |
A completed worksheet is evidence that participants considered a scenario. It is not proof that systems enforce access, preserve audit records or prevent unauthorized use. Record each control dependency explicitly: the owner, the system affected, the required approval and how implementation will be verified.
If a team creates draft working rules in the workshop, label them as drafts until the authorized organization owner approves them. A facilitator should not replace an employer’s legal, privacy or security decision-making.
Use a second scenario that differs from the demonstration. Ask participants to explain the data boundary, assign the reviewer and state when they would decline to proceed. Assess the reasoning and the action chosen, rather than asking only whether participants feel more confident.
For follow-up, the relevant owner can check whether staff know where to find approved tools and escalation routes. Keep unresolved cases visible. Do not convert a better quiz score into a claim of reduced regulatory risk without independent evidence.
The NIST AI Risk Management Framework organizes work through Govern, Map, Measure and Manage. It is a useful reference for structuring questions about ownership and context; it is not a certification conferred by a workshop. Apply your organization’s policies and obtain qualified advice for jurisdiction-specific legal requirements.
Use a fictional business scenario to identify permitted information, review ownership and escalation requirements. A policy checklist and risk-register exercise help participants record unresolved decisions instead of treating discussion as approval.
The workshop is educational. It does not establish legal compliance, provide certification or implement a complete governance system. Applicable obligations and formal decisions remain with the organization and its qualified advisers.
Start with a decision that currently delays work or creates uncertainty. Ask the business owner to define the task, and ask risk, compliance or information-security colleagues to identify the relevant internal requirements. Use approved policy extracts and fictional or sanitized examples so the workshop can examine the decision without exposing sensitive records.
Agree which questions the participants can resolve and which require a qualified specialist. At the end, record the decision, its owner, the supporting evidence and the unresolved issue. A workshop can surface gaps and practise escalation; it cannot provide legal assurance or certify that an organization is compliant.
| Planning question | Working output |
|---|---|
| Which AI-assisted decision needs attention? | A bounded scenario and named business owner |
| Which internal requirements apply? | Relevant policy extracts and questions for specialist review |
| What would trigger escalation? | A stop condition and named review route |
| What happens after the workshop? | An owner for each open issue and an agreed review point |
No. It can improve understanding, identify gaps and document responsibilities. Compliance depends on applicable obligations, approved policies, implemented controls and evidence beyond the workshop.
A useful scope includes reviewed scenarios, responsibilities, policy questions and an agreed next action. Exact deliverables should be specified in the proposal.
Yes, a cross-functional format can expose different interpretations of the same task. Define which participants own decisions and which contribute operational context.
No. A workshop is a learning activity that helps participants apply policies to scenarios, recognize gaps and practise escalation. An audit or legal assessment requires its own scope, evidence and qualified reviewers. Discuss those needs separately.
Preview the work · illustrative resource
A fictional procurement scenario shows how to record open questions and ownership. This is a learning example, not legal advice, certification or an expert-approved risk assessment.
For: Business, information and risk owners
A team wants to compare supplier proposals. One contains confidential pricing. Permission to use the chosen AI tool with that information has not been confirmed.
Risk: confidential information could be shared through an unapproved workflow. Evidence needed: the applicable information policy, tool approval and access controls. An unsupported claim that one supplier is “best” also needs correction.
Pause confidential inputs. The procurement lead and information owner confirm the permitted workflow and review standard. Record an owner and review date for each unresolved item. Training attendance does not approve the use case.
Ask for relevant subject experience, an example exercise and the proposed review approach. Check the facilitator’s named profile and agree who will assess the work. A profile or attendance certificate alone does not demonstrate results for your team.
Confirm the audience, permitted information, tools, accessibility, format, dates, fees, practical outputs and follow-through in writing. The examples here are learning materials; they are not client case studies or fixed delivery promises.
Read the AISFY founder profileShare the challenge, audience and skills you want to develop. AISFY helps you plan the learning and connect with relevant expertise.
Scope, facilitator, availability and fees are confirmed before booking.
Explore AI workshops ↗